John A. Ojabo — Senior DevOps Engineer
JOHN A. OJABO SENIOR DEVOPS & SRE
01 / EXECUTIVE PROFILE

Architecting for reliability, security & cloud velocity

A seasoned Software & Infrastructure Engineer with 6+ years’ expertise building, deploying, securing, and scaling mission-critical software and cloud infrastructure across AWS, GCP, and Azure. Specialized in Kubernetes orchestration (GKE, AKS, EKS), Terraform IaC, zero-downtime migrations, and site reliability engineering.

6+ YRS Engineering Exp
AWS · GCP · AZURE Multi-Cloud Platforms
99.99% Uptime SLA
1M+ Kubernetes Cluster Scale

Work Experience History

DevOps Technical Lead — Techsense Developers (Remote)
2025 – 2026
  • Led DevOps and cloud infrastructure work across multiple client projects, collaborating with software engineers and technical teams to design, deploy, troubleshoot, and scale production systems across Google Cloud and AWS environments.
  • Designed and deployed White Knight Law (whiteknightlaw.org), an AI-powered litigation assistance platform, on Google Cloud Run, implementing production-ready cloud architecture, secure configuration, containerized deployments, and scalable infrastructure practices.
  • Investigated and resolved a significant database performance and overload issue affecting JAPA.run, a production application experiencing excessive database load. Performed infrastructure and application-level troubleshooting, identified Hangfire background processes as a major contributor to database pressure, and provided technical findings and recommendations to address the underlying issue.
  • Managed cloud infrastructure across multiple client projects on Google Cloud and AWS, applying security, networking, deployment, and reliability best practices.
  • Collaborated with software and infrastructure engineers to resolve production issues and improve system reliability.
  • Built and maintained cloud-native infrastructure using Docker, Kubernetes, Terraform, CI/CD, and observability tools.
Google Cloud (GCP) AWS Google Cloud Run Kubernetes Terraform IaC Docker Hangfire Tuning MongoDB Atlas CI/CD & Observability
Senior DevOps Engineer (GCP) — Penningmeester.ai ABV, Netherlands (Remote)
2025 – 2026
  • Architecting scalable GCP-based infrastructure to support high-performance AI-driven financial systems (nerobudget.ai).
  • Implementing Infrastructure as Code (IaC) using Terraform for repeatable, secure, and compliant deployments.
  • Designing CI/CD pipelines in GitHub Actions and Cloud Build for faster release cycles and automated integration testing.
  • Integrating GCP Cloud Monitoring & Logging with Grafana, Prometheus, and Loki for real-time telemetry and incident triage.
  • Enforcing IAM policies, Workload Identity Federation, network segmentation, and Secret Manager to ensure strict data protection.
GCP Private GKE Terraform Kafka Cloud Build Grafana / Loki Cloud Security
GCP DevOps Engineer — NotJustEvent, Inc. (Remote)
2023 – 2025
  • Reduced operational cloud costs by $20K/year through static site migration to Azure Storage and spend optimization.
  • Led zero-downtime workload migration from GCP to Azure, improving application performance by 35%.
  • Built 6 CI/CD pipelines in Azure DevOps, accelerating software delivery velocity by 45%.
  • Deployed APIs via Azure API Management with 99.9% uptime SLA and automated Terraform provisioning (50% faster deployment).
  • Implemented Grafana, Prometheus, and Loki stack, reducing incident resolution time (MTTR) by 60%.
Azure DevOps GCP to Azure Migration Terraform Prometheus / Loki API Management
Azure DevOps Engineer — Keenchess (Remote)
2022 – 2023
  • Designed microservices architecture with Kafka & Zookeeper, achieving 99.9% uptime.
  • Migrated workloads from GKE to AKS, reducing costs and operational overhead by 30%.
  • Delivered auto-scaling AKS microservices with 99.95% reliability and automated CI/CD pipelines (20% faster deployment).
AKS Kafka / Zookeeper Kubernetes HPA Azure
AWS Kubernetes Administrator — Take & Trade Naija (Remote)
2021 – 2022
  • Deployed Amazon EKS cluster engineered for tournament trading platform with high availability and 99.99% uptime.
  • Reduced database query response times by 40% via Redis caching and PGbouncer connection pooling.
  • Implemented dynamic autoscaling that absorbs massive tournament traffic spikes and automatically scales down to minimal capacity when idle, significantly optimizing compute costs.
AWS EKS PGbouncer Redis Tournament Autoscaling
IT Support Specialist — Pittsburg Glass Workers (PGW) (Remote)
2019 – 2021
  • Administered Windows & Linux enterprise servers with strict focus on security compliance and Active Directory GPOs.
  • Configured Rapid7 for security monitoring, automated vulnerability scanning, and incident triage.
Linux / Windows Server Active Directory Rapid7 VDI

Featured Cloud Infrastructure Deployments

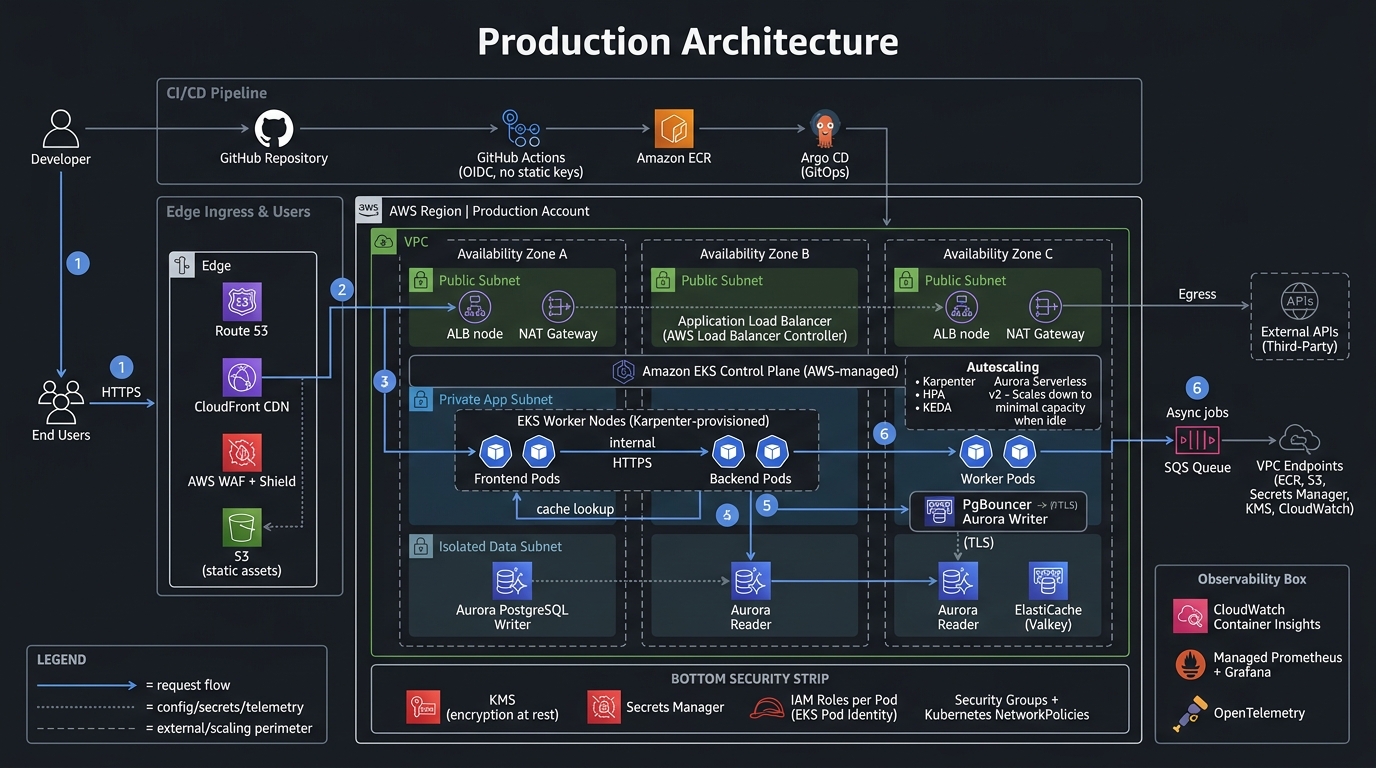
Take & Trade Tournament 3-Tier AWS Production Architecture Diagram
View Full Architecture Diagram
AMAZON WEB SERVICES (AWS) EKS TOURNAMENT PLATFORM 3-TIER MULTI-AZ

Take & Trade Naija — Tournament EKS Architecture

Production-grade multi-AZ architecture deployed on Amazon EKS for Take & Trade's high-stakes trading tournament. Engineered to handle traffic surges from multiple concurrent users during live tournament rounds, featuring rapid Karpenter node provisioning and automated downscaling to minimal capacity when idle to optimize infrastructure costs.

Edge & Ingress: Route 53 DNS, CloudFront CDN, AWS WAF + Shield, and S3 static storage routing traffic to multi-AZ Application Load Balancers (ALB).
Tournament Autoscaling: Amazon EKS with Karpenter (Spot + On-Demand node provisioning), HPA pod scaling, and KEDA queue-based scaling that scales down to minimal capacity when idle.
Data & Caching Tier: Multi-AZ Aurora PostgreSQL Serverless v2 (Writer + Readers) with PgBouncer connection pooling and ElastiCache (Valkey) low-latency cache for real-time leaderboards.
Security & GitOps CI/CD: Developer → GitHub Actions (keyless OIDC) → ECR → Argo CD GitOps into EKS; AWS KMS, Secrets Manager, and IAM Roles per Pod.
AWS EKS Karpenter Aurora PostgreSQL ElastiCache (Valkey) PgBouncer Argo CD GitHub Actions OIDC AWS WAF Tournament Autoscaling
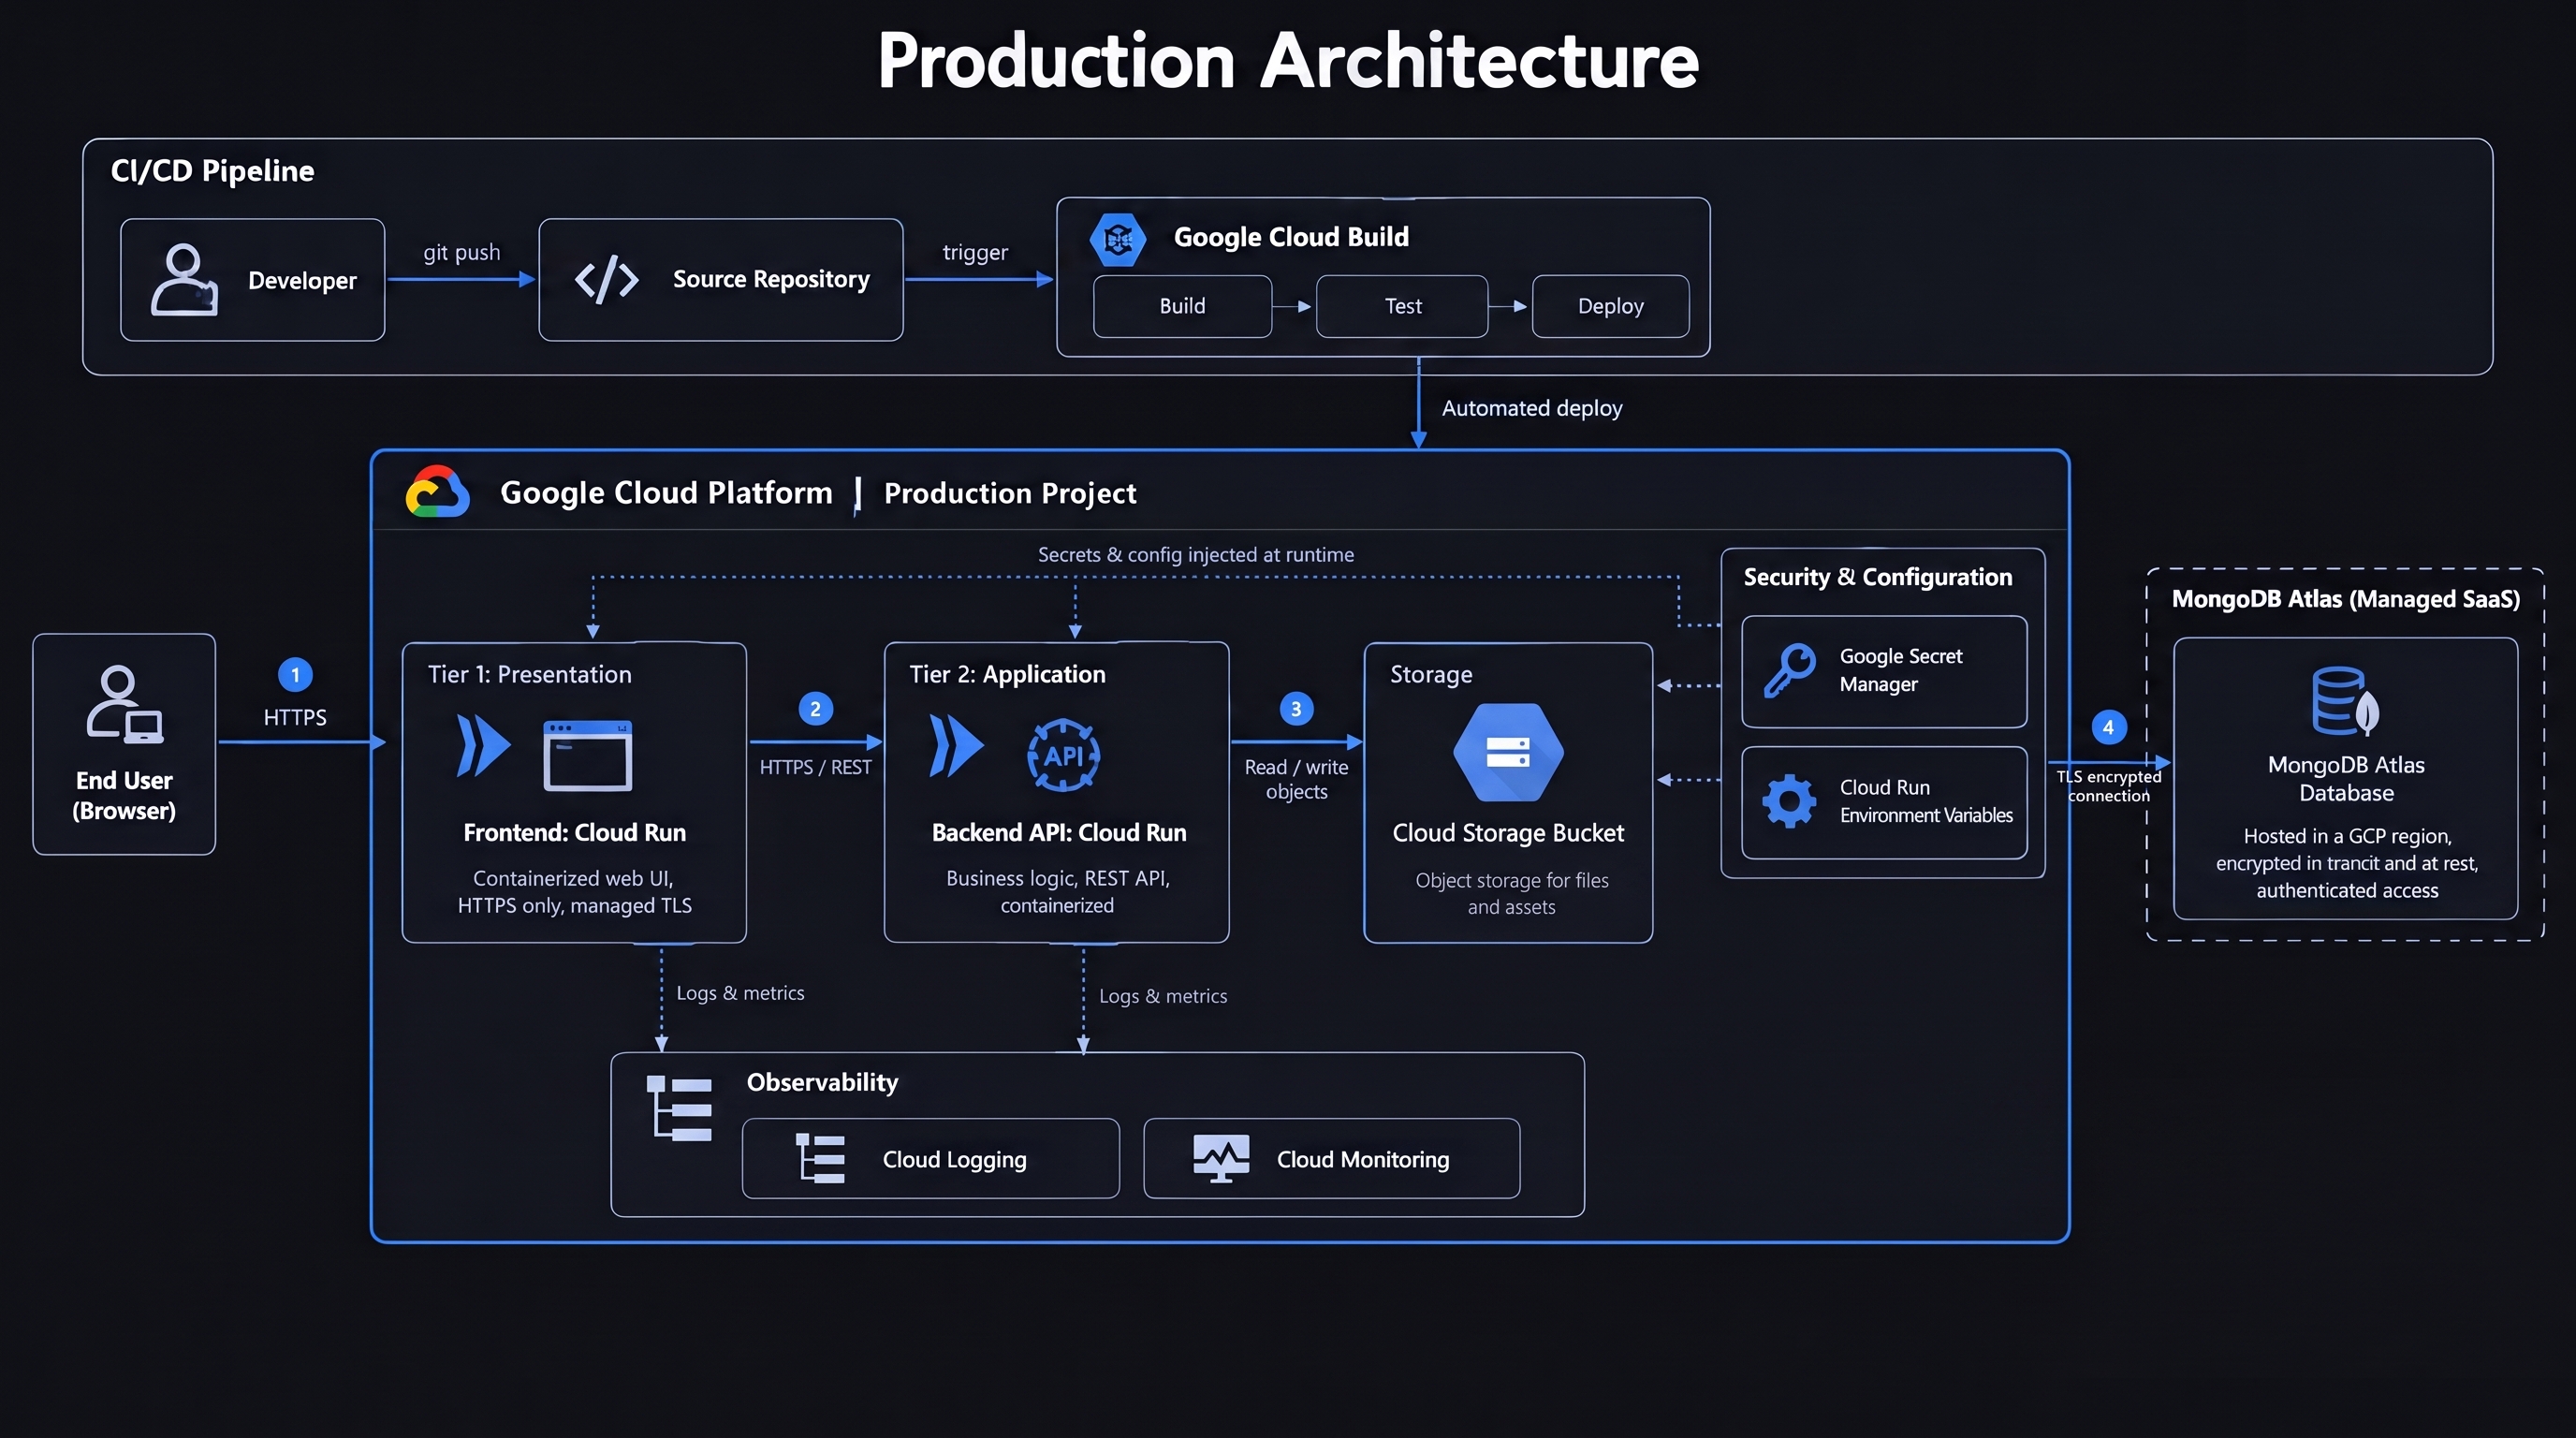
White Knight Law Production Cloud Architecture Diagram
View Full Architecture Diagram
GOOGLE CLOUD PLATFORM CLOUD RUN SERVERLESS whiteknightlaw.org ↗

White Knight Law — AI Litigation Assistance Platform

Production-ready cloud architecture designed and deployed on Google Cloud Platform for an AI-powered litigation assistance platform, featuring autoscaling serverless container services, automated CI/CD pipelines, and secure credential handling.

Ingress & Compute: Dual-tier Cloud Run microservices (Containerized Web UI Frontend + Backend REST API) with managed TLS and auto-scaling.
Database & Storage: Dedicated MongoDB Atlas cluster via TLS-encrypted connection + Google Cloud Storage buckets for legal document artifacts.
Security & Config: Google Secret Manager for runtime credential injection and isolated Cloud Run environment variables.
CI/CD & Observability: Automated Google Cloud Build (Build → Test → Deploy) from source repository with unified Cloud Logging and Cloud Monitoring.
Google Cloud Run MongoDB Atlas Google Cloud Build Secret Manager Cloud Storage Cloud Monitoring Docker
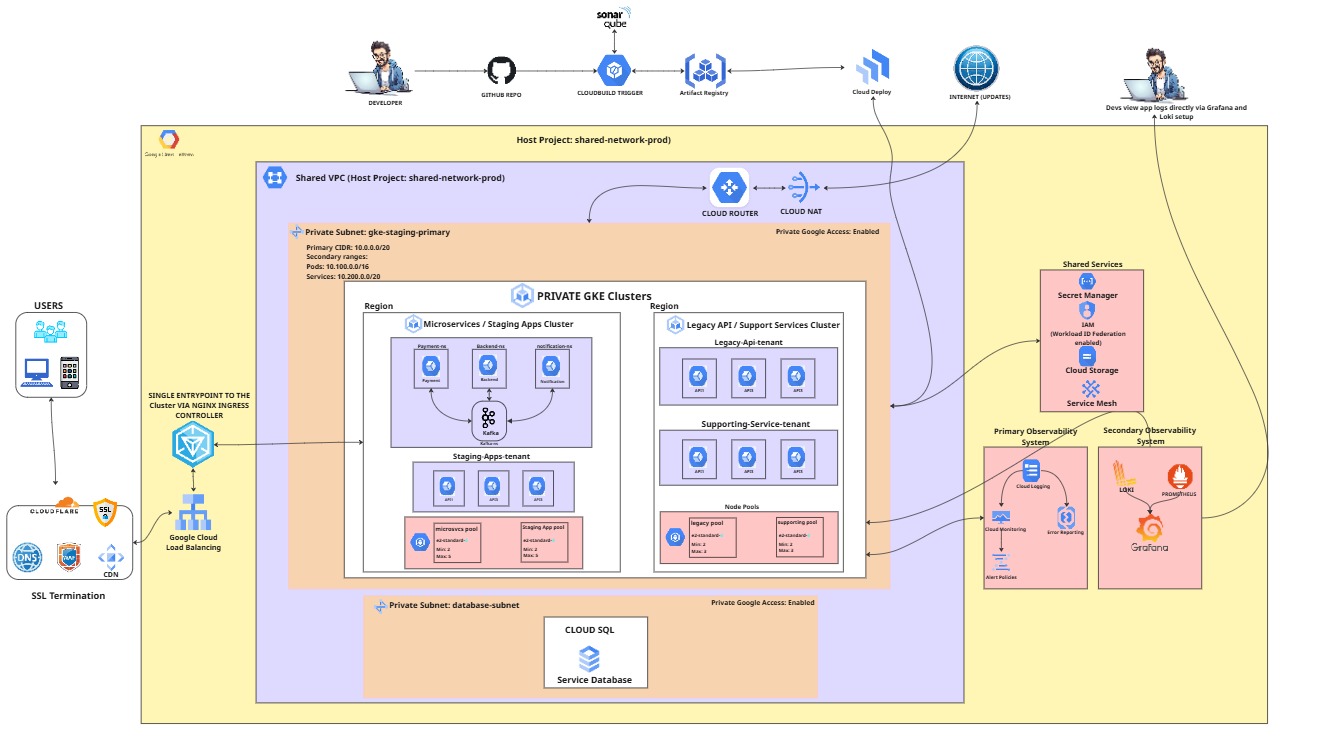
Penningmeester.ai Production GKE Architecture Diagram
View Full Architecture Diagram
GOOGLE CLOUD PLATFORM PRIVATE GKE CLUSTER nerobudget.ai ↗

Penningmeester.ai — AI Financial & Treasury Engine

Enterprise-scale multi-tenant private Kubernetes architecture deployed on GCP Shared VPC for high-performance AI financial analytics, high-availability event streaming, and strict zero-trust security isolation.

Networking & Ingress: Cloudflare WAF/CDN SSL termination → GCP Cloud Load Balancing → NGINX Ingress on Shared VPC (shared-network-prod) with Cloud NAT.
Private GKE & Kafka: Isolated subnets with dedicated microservices cluster (Kafka event bus, Payment, Backend) + staging/legacy tenant node pools.
Security & Storage: Cloud SQL database on private subnet, Secret Manager, Workload Identity Federation, and Service Mesh.
CI/CD & Observability: Cloud Build + SonarQube + Artifact Registry + Cloud Deploy; Dual Telemetry (GCP Monitoring + Grafana, Prometheus & Loki).
GCP Private GKE Shared VPC Kafka Cloud SQL Terraform Cloudflare WAF SonarQube Grafana / Loki
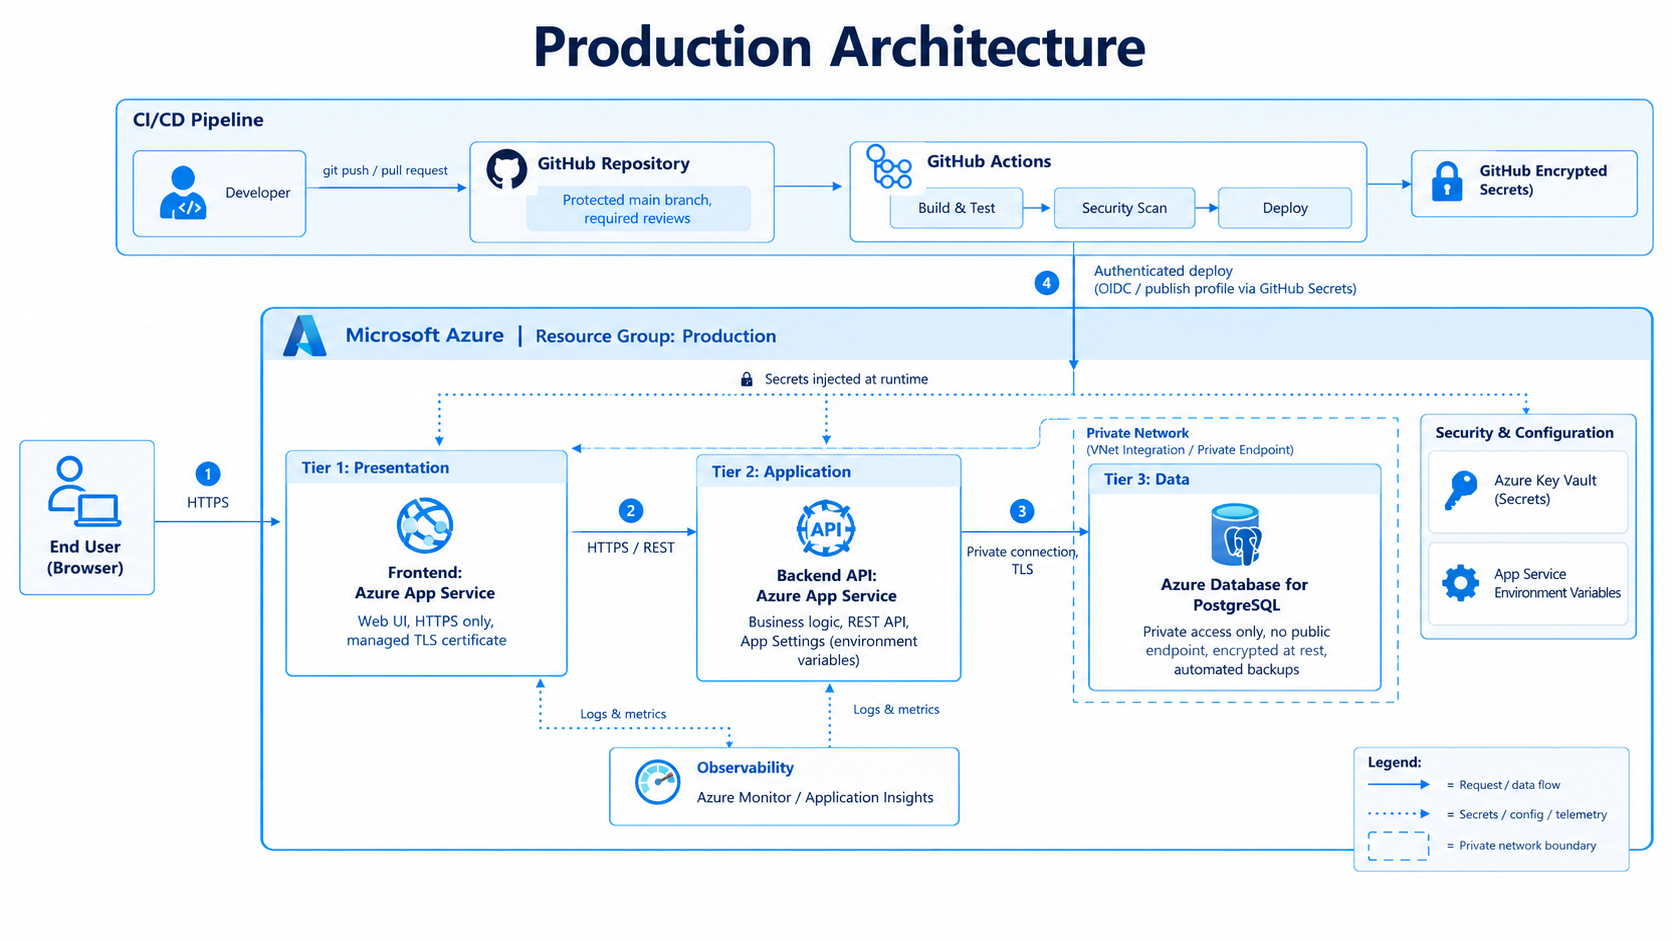
CV-AI Microsoft Azure Production Architecture Diagram
View Full Architecture Diagram
MICROSOFT AZURE 3-TIER PRODUCTION STACK

CV-AI — Enterprise Resume Optimization Platform

Highly secure and scalable 3-tier cloud architecture on Microsoft Azure for high-throughput AI document analysis and optimization, built with private networking, automated keyless CI/CD, and zero public data exposure.

Presentation & App: Dual Azure App Service instances (Tier 1 Web UI with managed TLS + Tier 2 Backend REST API for business logic).
Private Data Tier: Azure Database for PostgreSQL isolated in Private VNet via Private Endpoints (zero public IP, automated encrypted backups).
Security & Key Vault: Azure Key Vault for runtime secrets injection, strict RBAC, and encrypted environment variables.
CI/CD & Telemetry: GitHub Actions with automated security scans and keyless OIDC authentication; Azure Monitor & Application Insights.
Microsoft Azure Azure App Service Azure PostgreSQL Azure Key Vault GitHub Actions OIDC Application Insights Private VNet
Recon7 Autonomous Attack Surface Intelligence
FLAGSHIP OPEN SOURCE APACHE 2.0 CYBER RECONNAISSANCE recon7.ojabo.org ↗

Recon7 — Autonomous Attack Surface Intelligence

Defense-grade cyber reconnaissance and attack surface mapping platform. Orchestrates 12+ OSINT and vulnerability engines, builds correlated graph evidence ledgers, and enforces enterprise multi-tenant IAM isolation with asynchronous workers.

Engine Orchestration: Masscan, Nmap, Subfinder, Nuclei, Amass, and custom OSINT crawlers executing via async distributed workers.
Architecture & API: FastAPI asynchronous backend, React dashboard, Redis task queues, PostgreSQL knowledge graph, and Docker containerization.
Python / FastAPI Async Workers Docker React Redis Queue OSINT / Nuclei Multi-Tenant IAM

Skills & Certifications

Cloud Platforms & Serverless
Google Cloud (GCP), Microsoft Azure, Amazon Web Services (AWS), Google Cloud Run, App Service
Kubernetes & Containers
GKE, AKS, EKS, Docker, Helm, Ingress Controllers, Autoscaling (HPA, VPA, Cluster Autoscaler)
Infrastructure as Code
HashiCorp Terraform, Ansible, CloudFormation, Reusable Modular IaC
CI/CD & GitOps
GitHub Actions (OIDC), Google Cloud Build, Azure DevOps, ArgoCD, SonarQube, Cloud Deploy
Observability & Reliability
Prometheus, Grafana, Loki, Google Cloud Monitoring, Application Insights, Incident Triage
Security & Databases
Cloud IAM, Secret Manager, Azure Key Vault, PostgreSQL, MongoDB Atlas, Redis, PGbouncer, Hangfire Tuning
GOOGLE CLOUD
Professional Cloud DevOps Engineer
GOOGLE CLOUD
Professional Cloud Security Engineer
HASHICORP
Terraform Certified Associate
AWS
AWS Certified Cloud Practitioner
EDUCATION
BSc, Cyber Security — Miva Open University (2024–2027)
AWS re/Start Graduate — Cloud Fundamentals

Let's Build Resilient Infrastructure

Available for Senior DevOps, Cloud Architecture & SRE engagements.

LinkedIn ↗ Credly Badges ↗ [email protected]